also how did you test it locally?(not through jamf)
I run this policy once per computer during the initial setup. If the user wants to change it back I don't really care that much. To test it locally put that text into a script file that ends in .sh and then in terminal run
sudo sh /path/to/script.sh
It runs differently when running from Jamf though because scripts run as root and not as the logged in user. That's why you need the get logged in user and the sudo -iu $loggedInUser bit.
@jan.rosenfeld
that's a user setting and Jamf commands run as root. You probably need to do something like this:
EDIT: Set this up in a jamf policy and it worked on my machine.
#!/bin/bash

loggedInUser=`/bin/ls -l /dev/console | /usr/bin/awk '{ print $3 }'`
loggedInUID=$(id -u "$loggedInUser")

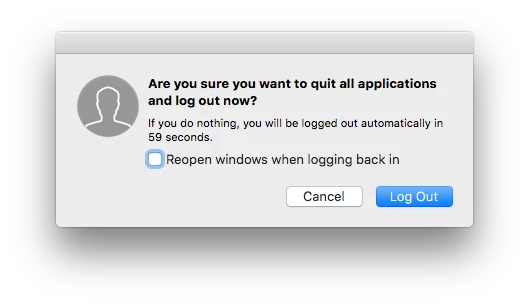
#Disable Reopen Windows When Logging Back In
/bin/launchctl asuser "$loggedinUID" sudo -iu "$loggedInUser" defaults write com.apple.loginwindow TALLogoutSavesState -bool false

exit 0
Hey, Adam. Been wanting to look at this for a while. I run this script and it runs successfully. But nothing changes. Do I need to plug the acct name of the logged in user as a variable? Thanks!