Get Support
Recently active
Hi,We are using SYM which is working perfectly however we need to set the default font for Outlook, Word, Excel and PowerPoint. Has anyone been able to achieve this? TIA.
We're using Jamf Now with Jamf Protect enabled and periodically seeing CPU spikes (with the process hanging and eating up resources indefinitely) caused by the com.jamf.protect.security-extenstion. This is actually causing the OS to get unresponsive and overheat, eating up all available CPU. The simple solution is to kill the process, but eventually the problem comes back. Some basic debug information from the pid on a machine from when the problem occurred: sudo dtruss -p 337 dtrace: system integrity protection is on, some features will not be available SYSCALL(args) = return sigreturn(0x700008F16550, 0x1E, 0x1F99DBCB69B66C71) = 0 -2 sigreturn(0x70000909F568, 0x1E, 0x2EECB3AAFCC39E5E) = 0 -2 sigreturn(0x700008F16550, 0x1E, 0x5ECF2791121B465B) = 0 -2 sigreturn(0x70000909F568, 0x1E, 0xDCFC18327AB19367) = 0 -2 sigreturn(0x700008F16550, 0x1E, 0x131DCCD7A886722F) = 0 -2 sigreturn(0x70000909F568, 0x1E, 0xA6420414AE3C2D83) = 0 -2 sigreturn(0x700008F16550, 0x1E, 0x77
Hi,I would like to create a deployment for Maya 2025 based on the topic for 2024:https://community.jamf.com/t5/jamf-pro/packaging-autodesk-maya-2024-with-redundant-license-servers/m-p/298743I've found a .app installer in the Contents of the installer:/tmp/maya2025/AdskIdentityManager/AdskIdentityManager-Installer.app This app opens an installation wizard. How can I execute this (after the PKG installs) in silent mode?Thank you.
Getting kicked out of Jamf Pro server. If you are experiencing a similar issue here is my ticket number: 19843077 After enabling the SSO I am getting kicked out of the Jamf server multiple times daily.Behavior:clicking on a link presents signed out pageoractively browsing a page and presented singed out pageBrowser:SafariChromeOS: 15.4 (scheduled the update for later in the week)
Setting up some new M4 airs. Made a mistake after enrollment with the account that was created so decided to wipe and start over. Ran the Wipe command and instead of what I’ve seen with previous devices this one when to activation and then Recovery so that the macOS has to reinstall. Is this expected with M4’s?? The M2’s went to activation and then right to setup.
Hello,I have noticed recently that searching for JAMF Nation articles on any mainstream search engine gives the results for those articles, but if you click them it brings you to the JAMF Nation home page instead of the article trapping the information behind the built in search.Is anyone else having this issue, or know what this is? Thanks
Hi All,Not sure how many of you use Clearpass and JAMF but I have been able to modify the script provided by clearpass to collect the rotating MAC address of the device so that clearpass will recognise it and be able to assign a policy for the device without having to turn the rotating MAC address off. The script is below, all you need to do is update the cppm-all-mac-addresses extention attribute script with the one below…. #!/bin/bash wifi_interface=$(networksetup -listallhardwareports | awk '/Hardware Port: Wi-Fi/ {getline; print $2}')rotating=`ifconfig $wifi_interface | grep ether | cut -d ' ' -f2` result=`/usr/sbin/networksetup -listallhardwareports | /usr/bin/awk '/Ethernet Address/ {printf "%s%s",sep,$3; sep="|"} END {print ""}'` echo "<result>$result|$rotating</result>" a few things to note… This will only work for MacOS devices and not iOS Depending on what time the machine checks in and the clearpass does a JAMF update (every 30 mins) it can take some time to get
Hello,I just set up SSO in Jamf Account.I'm not sure where I need to grant administrator privileges to your Identity Provider (IdP) to configure a connected app and assign the relevant users and groups.
Hello,We are transitioning part of our fleet from AD binding to jamf connect; however, we have hit an odd snag. In the past, we'd be able to just install jamf connect and once the user logged in, it would demobilize their account and sync with their entra credentials. With this new batch with JC 2.37, the accounts become Local, however they then get locked. When a user tries to log in with Entra SSO, it loads, looks like it has accepted the credentials but then just returns to the login screen. It does not accept any password with local login aswell. One thing to note, the devices are not on premise when the change takes place, if that has any effect. If anyone has seen this and has a fix, it would be much appreciated. -Jack
Hi everyone, I’m currently exploring the possibility of deploying Jamf Connect in our organisation. I have setup the SSO in Jamf Account to point to our EntraID tenant and it’s working fine to login users in both Jamf Account and Jamf Pro Cloud. All the documentation seems to suggest that I need to configure another app in Entra ID to allow Jamf Connect to authenticate users but since Jamf has introduced the Jamf Account OIDC SSO to try and harmonise things, I’m wondering if I can just point Jamf Connect at that rather than creating a new app. Can this be done or am I misunderstanding how the OIDC SSO connection works in Jamf Account? Thanks,Kieran
I was not going to be able to go to JNUC 25 on my own and my job doesn’t have the resources to send me. Today I found out that I have been awarded the “JNUC ‘25 | Diversity Sponsorship”. Being a newer JAMF Pro Admin, I am incredibly stoked to have been giving this opportunity!! I just wanted to put this into the universe so I could connect with some folks before the conference. I would also love to connect with any other Scholarship recipients.Can’t wait to meet you all!!!
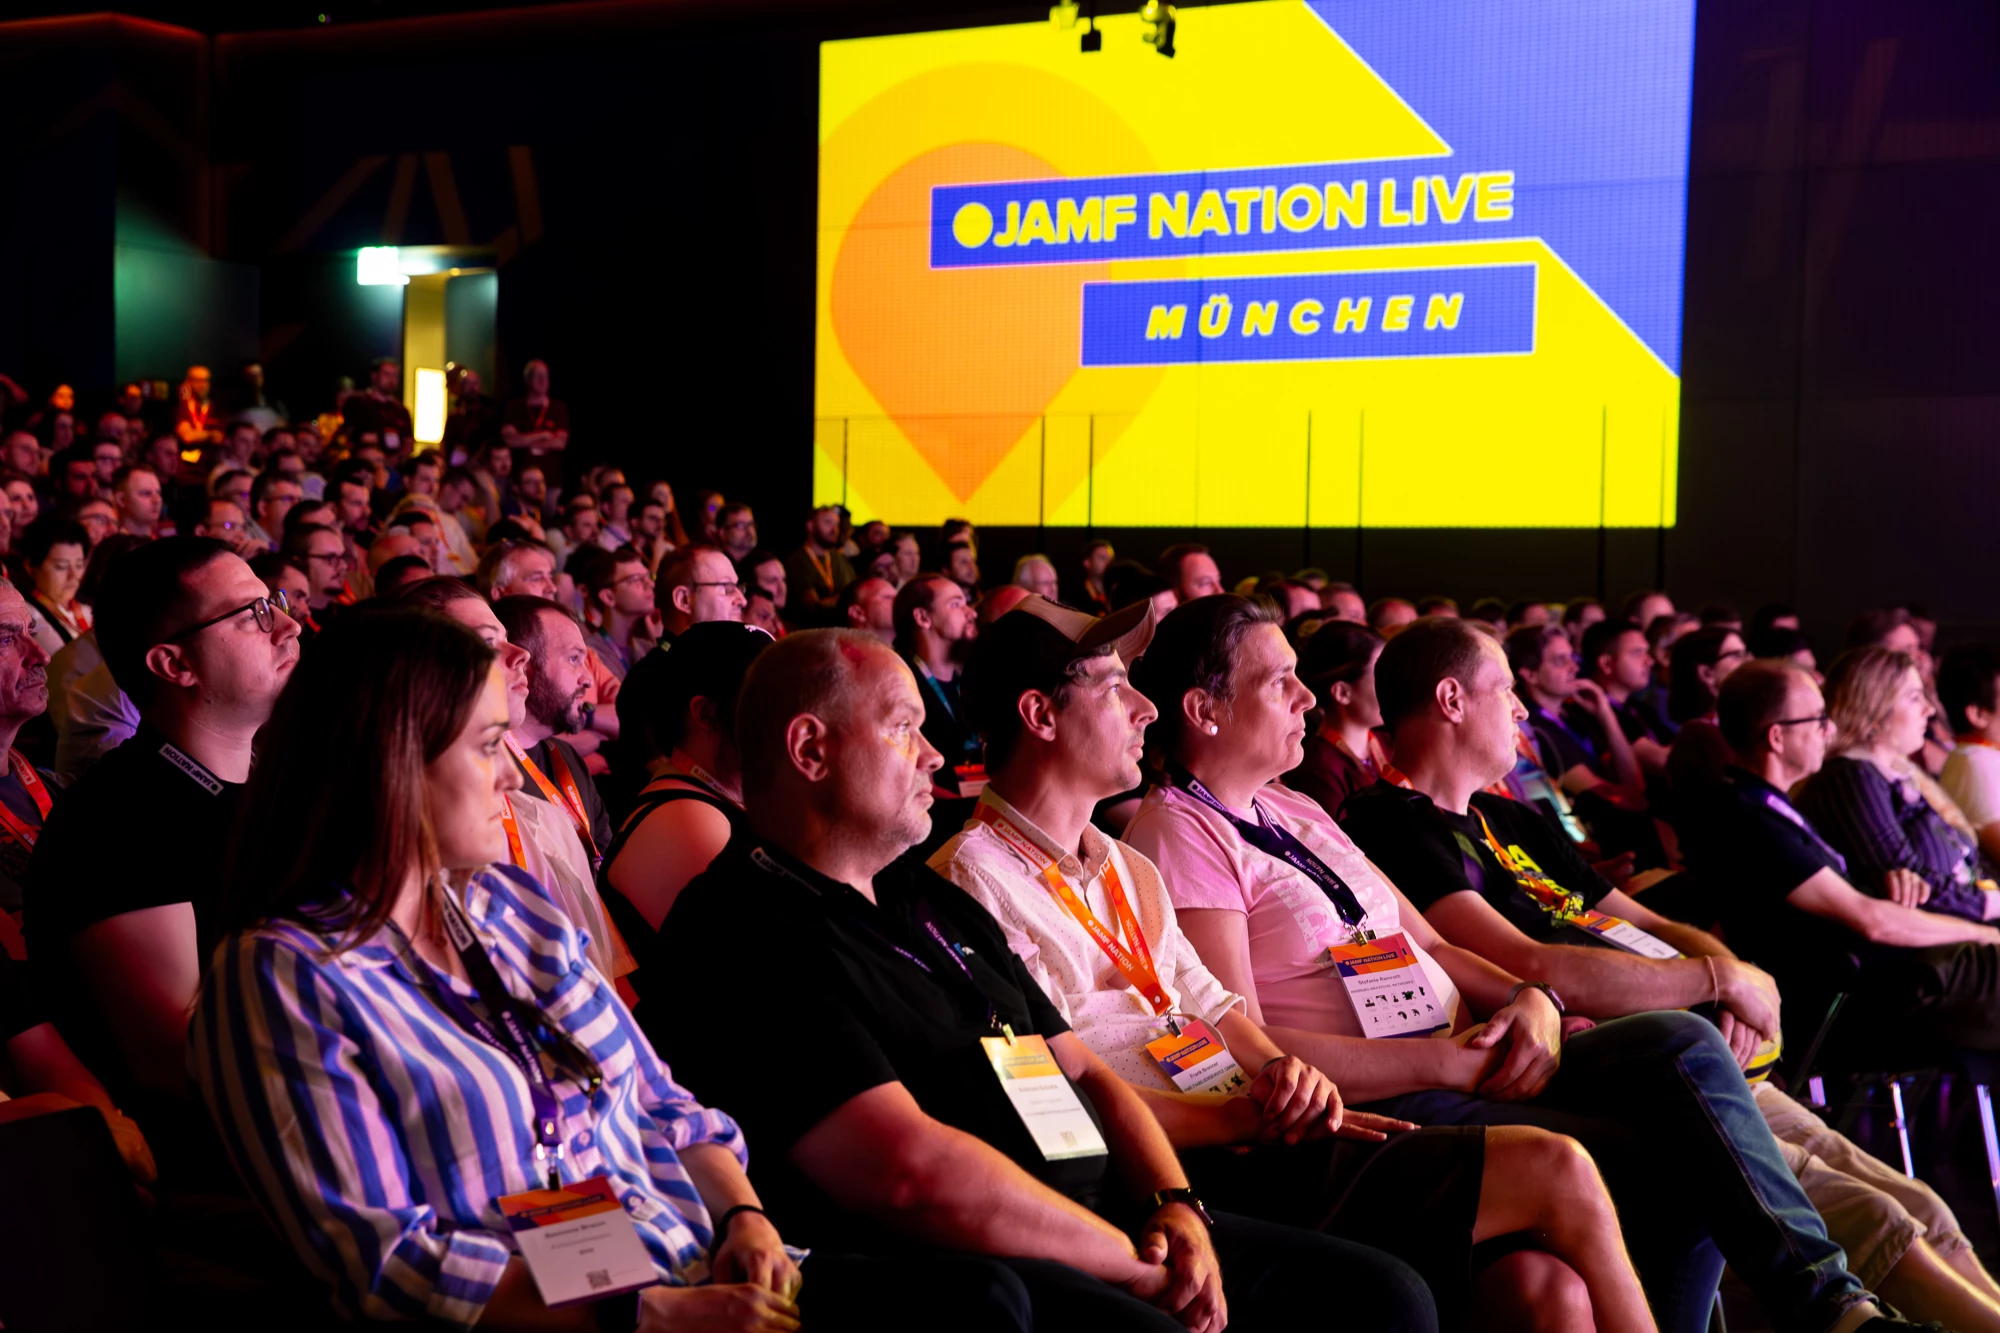
On June 24th, I attended Jamf Nation Live in Munich – and I'm still buzzing with excitement.Jamf has once again demonstrated why it is considered the leading provider in the Apple enterprise environment. I found the new developments around Jamf Pro particularly exciting, including improved integrations with Microsoft Entra ID, automated compliance checks, and even closer integration with Apple Business Manager. For businesses, this means less manual work, greater security, and easier scalability. Above all, the new self-service features give IT teams more control while giving end users more flexibility—a real productivity boost. In addition to the technical innovations, the exchange with the Apple Admin Community was the real highlight for me. I saw many familiar faces and made new contacts. What always impresses me is the exceptionally open and helpful atmosphere in the Apple world. People share scripts, best practices, and solutions without any sense of competition—that's really uni
I am trying to package up Mudbox 2026 using below script. However the app does not install when I run the package for Mudbox. Any ideas? #!/bin/bash #Copy installer app from .dmg to /tmp#Modify values below as necessary (Usually: year and pKey) #Set variables year="2026"pkgPath1="/private/tmp/InstallMudbox2026.app/Contents/Helper/Packages/Mudbox/Mudbox_core2026.pkg"pkgPath1="/private/tmp/InstallMudbox2026.app/Contents/Helper/Packages/Licensing/AdskLicensing-15.1.0.12339-mac-installer.pkg"pkgPath2="/private/tmp/InstallMudbox2026.app/Contents/Helper/Packages/Licensing/adskflexnetserverIPV6.pkg"pkgPath3="/private/tmp/InstallMudbox2026.app/Contents/Helper/Packages/Mudbox/Mudbox_AdLMconf2026.pkg"pkgPath4="/private/tmp/InstallMudbox2026.app/Contents/Helper/Packages/Mudbox/Mudbox_core2026.pkg" mudboxpKey="437R1"networkServer="Network License Server"mudboxlicPath="/Library/Application Support/Autodesk/AdskLicensingService/${mudboxpKey}_${year}.0.0.F"mudboxlicFile="LICPATH.lic"mudboxlgsFile="L
When adding apps to Self Service (or even Self Service+) via Mac Apps, the applications descriptions are in German. I’ve ensured that English is set to the preferred language and enabled location service. This is being run on a test VM but I can’t for the life of me figure out why this would be the case?
We wanted to share a few updates about new features in Jamf Account that improve SSO management and troubleshooting, as well as new documentation resources for enabling OIDC authentication for platform services.A new Jamf Account Release History section in our Learning Hub details several improvements:A new "Authorize URL" button for Google Workspace OIDC connections, enabling consistent group support across organization types Login History tab under Profile, allowing you to view authentication history and ID tokens when using an IdP Enhanced error handling with unique reference UUIDs for failed SSO attemptsTo help customers migrate to OIDC, we've published a SAML to OIDC Migration Guide that walks through adopting OIDC-based workflows.The Understanding SSO Authentication Methods guide helps address common questions about IdP choices, OIDC benefits, and authentication options. It includes visual breakdowns of both SAML-based and OIDC-based authentication methods to demonstrate how vari
We recently migrated to Jamf Cloud and using Azure AD as our Cloud Identity Provider and Single Sign-On solution. It works well enough, but we have a weird situation. We're sticking pretty close to Microsoft's documentation on it, which can be found here.By default, the iDP maps userPrincipalName as the username. That's a full email address in our environment, so we want to use onPremisesSamAccountName instead. That works fine in the iDP in both testing and looking up users/accounts.We also need user authentication during the initial device enrollment via DEP. We've gotten that added in by adding an Enrollment Customization that is just the SSO.Here's where it gets dumb. If we now enroll a machine while the User Name mapping is set to onPremisesSamAccountName, the SSO during enrollment registers the device to just the userPrincipalName with no other user data. The Pre-Fill Primary Account Information only puts in the userPrincipalName as the Us
Hello,on macOS 14, With PPPC Utility, i want to create a profil who allow the usage of camera and microphone on an .app. But when i open PCCC Utility or make it across web admin from Jam, there is not “Allow” option available in the select field.I read that the application must be without hardened runtime, but if i remove the hardened runtime, the app can’t be export via “Archive” → “Direct distribution”.Any idea ?
Heya awesome Mac admins! I am still relatively new to this whole Jamf thing and looking into setting up Jamf Setup Manager to install our apps before the user reaches the desktop. I am trying to follow guides and getting hung up quite a bit on step 1 of most them, “package Setup Manager”. This is kind of a loaded step. I have tried several ways of doing this. I have packaged the zip, which didn’t work. I have extracted the .zip to the desktop and then packaged, didn’t work. I have tried putting the extracted zip in different folders, then packaging from there with Composer, didn’t work. How the heck do I package this thing for deployment? The configuration from Jamf Pro is relatively straightforward, I just need some help making sure the actual files are in the proper places.
Question for how/if we have controls to deploy a specific app version to iPads. We have a couple applications we use and work closely with the developer and schedule when we make the update available on our EFB iPads. We use the check boxes ‘Schedule Jamf Pro to automatically check the App Store for app updates’ and ‘Force App Update’ to accomplish this. Today is the first time we noticed a different version was installed than what Jamf Pro is reporting as available.This is what is showing under Mobile Device Apps.Does it always install the newest version of what’s available in the Apple store via Self Service regardless of what Jamf Pro is reporting? When looking at the Inventory for the iPad we see that 10.5.1 was installed.
CIS 1 Allow Touch ID to unlock your mac what needs to be deactivated?Hi Hope you can help, how do we allow users to use Touch ID rather than the full password each time sleep is activated. What needs to be unticked in the list of Managed Rules in compliance?Thanks
Hello there, Is there any way to automatically enable Location Services for non-admin users? I know it is currently not possible to set up a PPPC, so I tried some scripts to enable this feature. For example: #!/bin/bash #set -x ########################################################################################## ## ## Script to enable automatically Location Services on Mac ## ########################################################################################## ## Define variables location_enabled=$(sudo -u "_locationd" defaults -currentHost read "/var/db/locationd/Library/Preferences/ByHost/com.apple.locationd" LocationServicesEnabled) ## Check if location services is enabled. If so, we will terminate this script immediately. Otherwise, we will enable it. echo " $(date) | Checking if this macOS-device has Location Services enabled or not..." if [[ "$location_enabled" = "1" ]]; then echo " $(date) | Location Services are already enabled" exit 0 else ech
We've followed the steps given in this guide (https://www.jamf.com/blog/help-users-activate-microsoft-office-365-and-configure-outlook-in-one-click/) but when we launch Outlook, our email address isn't automatically populated like it is here. Has anyone else experienced this? If so, what was your workaround? Any advice would be much appreciated! Thanks in advance!
Hi folks, I’m trying to find a way to report (at the very least) which of our devices have Jamf Connect enabled in System Prefs>Privacy & Security>Local Network. Based on my investigation, it seems like SIP/Apple blocks this particular preference from being viewed or modified by MDM’s (on macOS 15+). I have seen similar discourse around the weekly system prompts for Camera/Screen recording and some solutions there, but nothing for this. I am preparing to upgrade all of our Macs to Sequoia 15.5, about ~80 computers. My org uses Entra for login + network drives and I’ve found that end-users on Sequoia that don’t have this enabled have issues with password sync and accessing the drives. Grateful for any input or advice!
I have Jamf connect configured with entra ID and requires authentication with their network account at each restart. My users are unable to sign into their macs offline because the account cannot authenticate with microsoft. Is this a setting within jamf connect that I can change to allow a local account to pass through when not connected to internet?
Hi, Jamf Nation! Many of you wear multiple hats and are the glue that holds the technical processes together in your environments. That’s why when something goes wrong, you need us, your Jamf Support team, to be by your side. Today we’re excited to share that the Support service you rely on is getting even better by streamlining your access to Jamfs who can best help you solve your problems at the right time. While all of the details of the enhanced process are in your email inboxes, we’re happy to share the highlights here. Knowledge and support now live together in the Support Portal, which is accessible via Jamf Account or at support.Jamf.com. Customers will see an updated chat experience (with more enhancements to come) The Product Issue process was simplified to enhance the customers’ overall interaction with Support While this work greatly enhanced the support you’ll receive from us, the majority of the changes are on our side (within the Jamf “walls”). Our Support teams w
Earn a cool badge and Jamf Nation Reward Bytes for your published articles. We’re looking forward to your submissions!