Get Support
Recently active
We need to add a new allowance to our VPN profile that is required for the newest version of our VPN client .I am trying to figure out what exactly happens on macOS when a profile gets updated. Does it remove all the settings the profile sets and reapply, or does it only add/remove changes. I would like it so people do not get kicked off VPN when the profile is updated (The addition to the profile only deals with login items.
Just to be clear this is not a JAMF issue or any MDM issue. This is an apple issue and unless people speak up by opening apple tickets or feedback cases or talking with their apple engineer, apple will not take this seriously.If you as system engineer of your environment would like IP addresses reported from your devices please feel free to use as much or as little of my argument to apple from my ticket I opened with them I am writing to advocate for the inclusion of IP address reporting within MDM solutions for devices supervised under the DEP for iOS, macOS, visionOS, and tvOS.The ability to report IP addresses is not merely a desirable feature; it is an essential capability for enterprises to gain a comprehensive understanding of their devices and network environment. This functionality will significantly enhance our ability to scope and troubleshoot Apple devices effectively. Currently, the process involves multiple teams and systems to ascertain a device's IP address, which requi
Does anyone receive these emails, [HIGH] Alert for Sophos Central, when their computer is updated from one operating system to another, or at other random times? I was informed by Sophos that I would need to manage using static groups instead of smart groups, but that seems inefficient and not ideal.
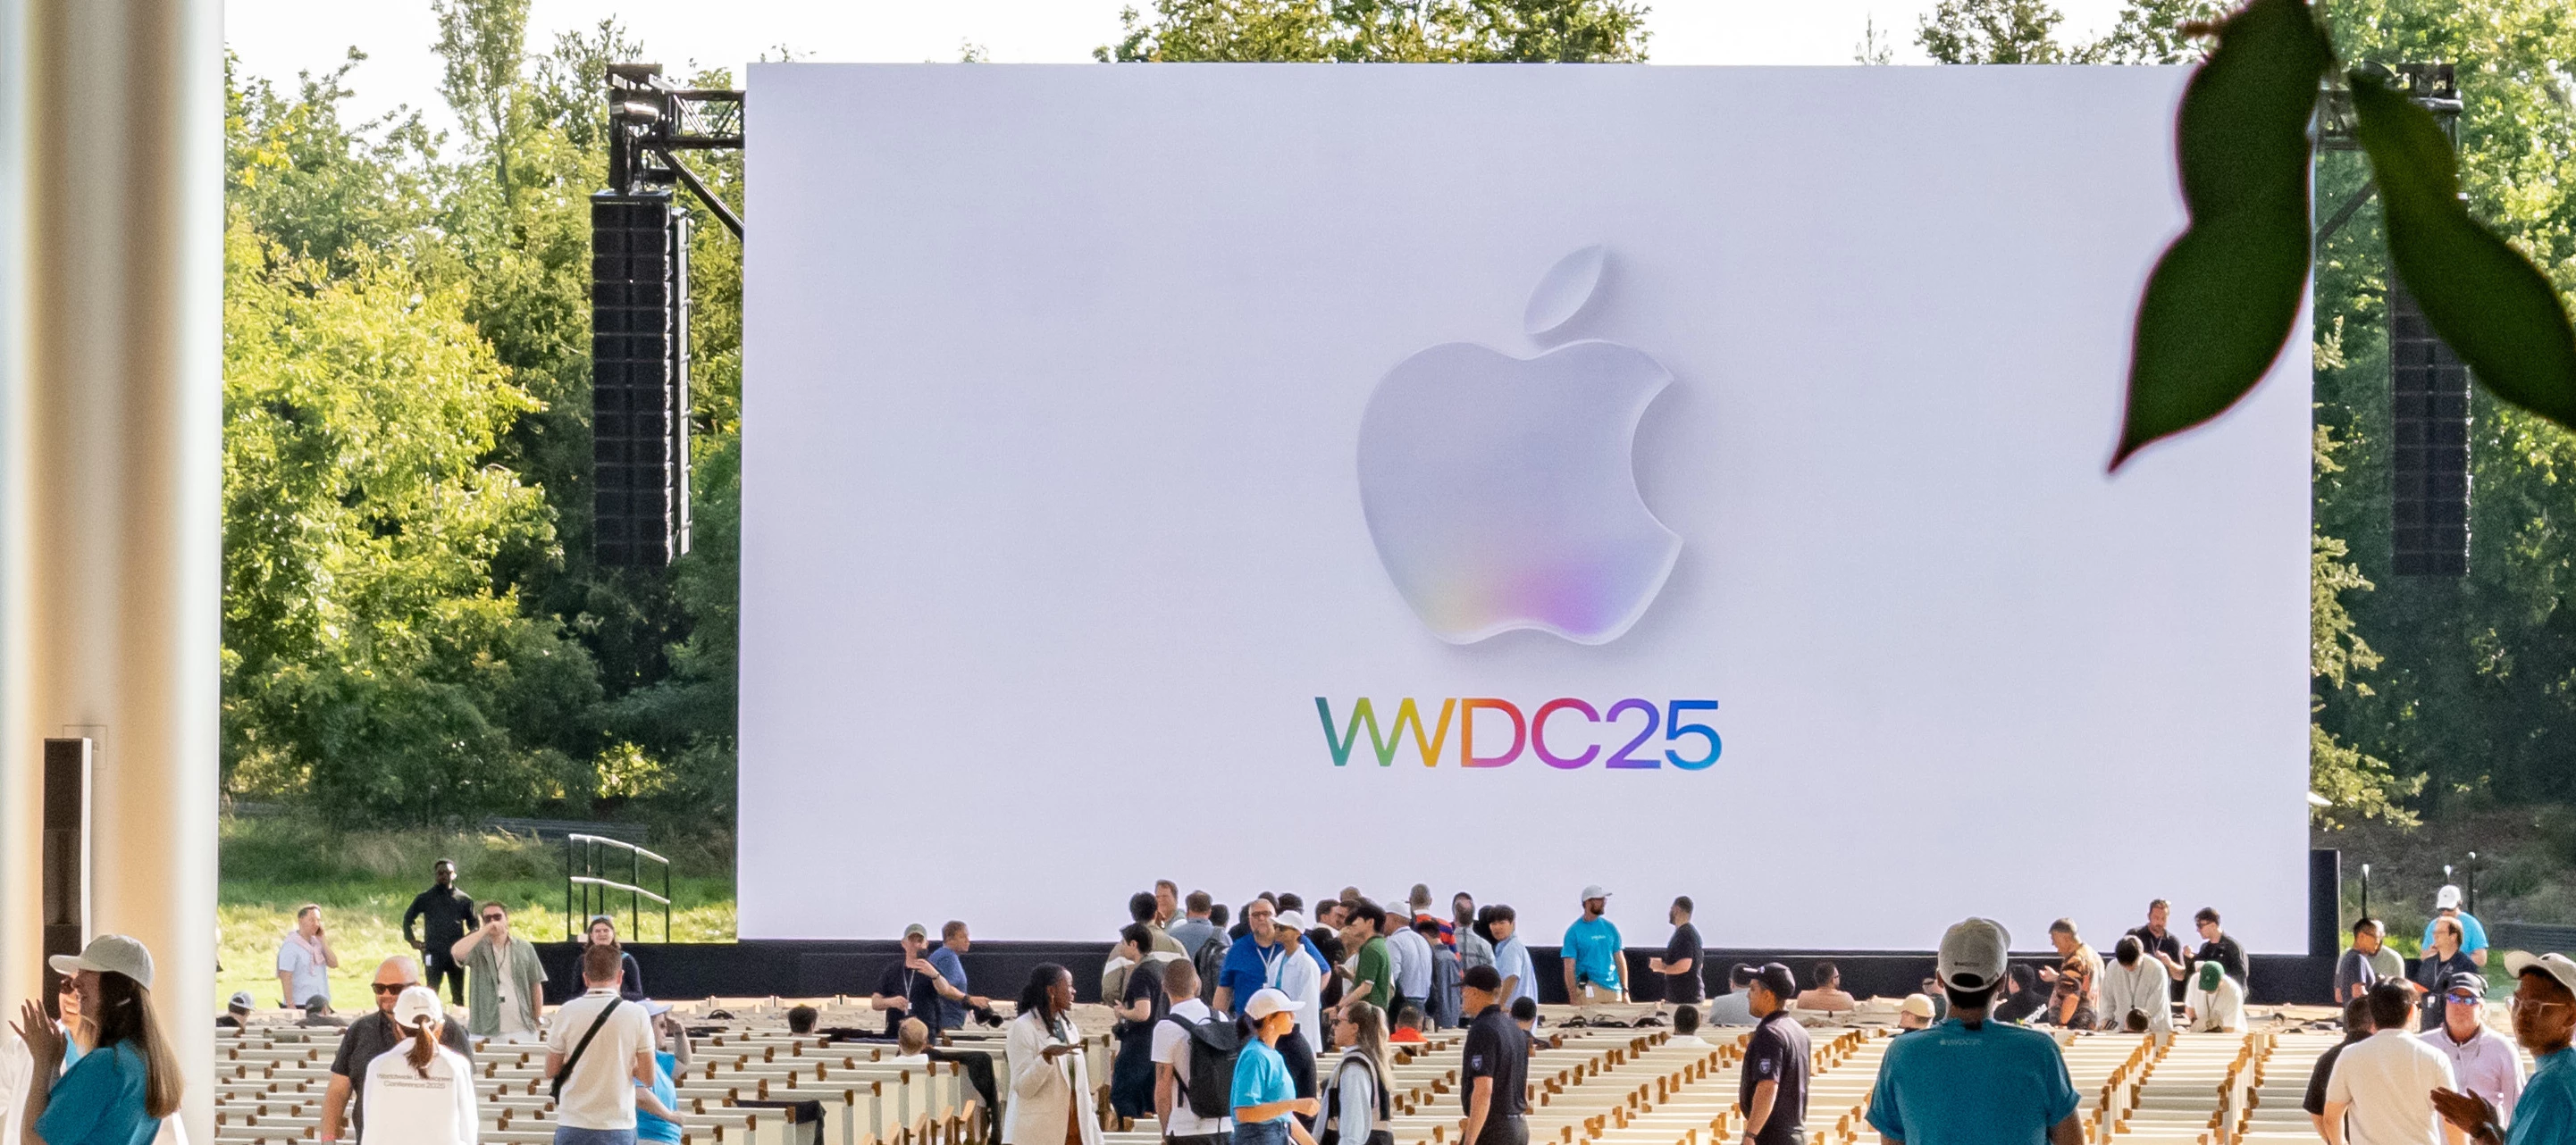
Monday June 9 it was that time of the year, Apple’s World Wide Developers Conference kicked off with the usual Keynote where they introduce the new versions of macOS, iOS, iPadOS, visionOS, tvOS and watchOS. I was lucky enough to have obtained a ‘golden ticket’ through the lottery system and actually attend this event at Apple Park in Cupertino! As an Apple consultant and macOS developer at long-time Jamf-partner Root3, it was both very exciting and relevant for me to attend. I’d like to share my in-person experience while also highlighting key announcements, especially for Apple IT admins and how this may affect us this fall. In-person experienceThe WWDC event for attendees is actually a multi-day event with most activities taking place from Sunday to Tuesday. It starts with a welcome reception at the historic Apple Campus at 1 Infinite Loop where you check-in, get your badge, happy Apple employees high-fiving and lots of photo opportunities. It’s a great start of the week to mingle
Things are a little different around here! As we shared in this Tech Thoughts article, any posts that were created in that space between JUNE 23 - JULY 3 DID NOT MIGRATE. Instead of putting Jamf Nation into read-only mode during our transition to this new site, we opted to keep it open so y’all could keep getting help from the community. If you posted during that timeframe and didn’t get your answer, go ahead and re-post it on the forum now! If you posted during that timeframe but already got your answer (or don’t need it), no need to do anything else. That’s all! I hope you’re enjoying this revamped version of Jamf Nation. Be sure to reach out to us at jamfnation@jamf.com with any questions or feedback!
Today we released Jamf Connect 3.1.0; this release addresses the following product issues:[PI131938] Fixed: For configurations using Microsoft Entra ID as their identity provider, the Jamf Connect login window displays an error message at the bottom of the screen when passkeys are an available authentication method. [PI134695] Fixed: The Jamf Connect login window displays a black screen after a user enters their password incorrectly and triggers the maxFailedAttempts setting. [PI135947] Fixed: When Short Name (OIDCShortName) is set to an email, the Jamf Connect login window creates a user account with the entire email domain instead of the prefix before the "@" symbol. To access new versions of Jamf Connect, log in to Jamf Account with your Jamf ID. The latest version is located in the Solutions section under Jamf Connect.Product DocumentationFor additional information on what's included in this release, review the release notes via the Jamf Learning Hub.
Today we are releasing a maintenance version of Jamf Pro; highlights include:Changes and ImprovementsJamf has upgraded the Jamf Support ticketing system. To access the new Support portal, log in to Jamf Account and click Contact Support in the top navigation. Jamf Pro no longer returns a "Version entered is unknown" error when attempting to execute an advanced computer search or save a smart computer group that uses 'unknown version' as a value for existing patch reporting criteria. Resolved IssuesJamf Pro Server: Security IssueJamf provides the CVE-ID for security issues with high or critical severity when possible.[PI136944] Jamf Pro 11.18.1 includes Tomcat 10.1.42, effectively resolving a known security vulnerability in a third-party library (CVE-2025-48976). For additional information on what's included in this release, review the release notes via the Jamf Learning Hub.To access new versions of Jamf Pro, log into Jamf Account with your Jamf ID. The latest version is located in the
Hi,I’m trying to use Network Access in Jamf Cloud to route traffic to M365 apps via the ZTNA network for IOS devices. I’ve added this as a separate Activation Profile on top of the Default Profile that covers different services. The users already had the Jamf Trust app on their phones for the previously enabled services. Those services didn’t require a login, since Jamf Pro is distributing Jamf Trust. With the additional profile I assumed that logging in was somehow made possible in the App, but there’s no option anywhere. Also, I don’t see that traffic is routed through the ZTNA network either (since I would expect traffic to come from a different IP). Last, if I look in device management in Jamf Cloud, the Network Access services is not active for the devices, so I wonder if the Activation Profile is even deployed, despite I’ve done that (I even tried to open the link on a phone manually).Any suggestions on what I might be missing or doing wrong? The documentation isn’t really giving
We’ve been testing Platform SSO with Microsoft Entra ID in a Password Authentication configuration, and found that we need to create a local account on the system first in System Settings > Users & Groups, before a user can log in with user@domain.com as their username, is that expected behavior? If that is what is required then we can work with that, but ideally once the system has the relevant configuration profiles installed I’d like anyone in Entra ID to be able to log in without any manual configuration. If I don’t manually create a local, standard account with the same username beforehand, the user just gets a dialogue box containing a yellow warning triangle with no other information and is then automatically logged out again. Or would I be better off with a Secure Enclave configuration? We have hundreds of staff 1:1 Macs (mostly MacBooks) and about 100 lab iMacs/Mac Studios. We are a big MS/Azure/Entra house, currently bind to AD (which we are desperate to come away from
Hello jamf nation, If the goal of the new Jamf Nation Rewards program is to generate more content, user numbers and traffic, then it would be cool if jamf also considered redesigning the forum page. There are no specific topic areas. I can only search or scroll down. If I have then scrolled down so far that I have to click on "load more", then open a post and click back again, I am back at the top of the homepage and have to go back to the bottom and click on "load more". The only way to avoid this is to open a post in a new tab. Are there any thoughts on this?l @Mitchell_Gordon Cheers
is there any way to create an extension attribute that will contain audit of usb devices (storage) connected e.g. in the last month?
We have been using this profile to automatically connect to the corporate SSID. However, two days ago, I encountered an issue when I attempted to re-push the profile to a device—it failed to install. Upon investigating the profile, I noticed an "Options" error that appears when the SCEP payload is selected. However, no specific errors are shown in the payload settings themselves. I tried to create a new profile but still error is there Could you please assist in identifying and resolving the issue?
Does anyone noticed LDAP attributes for Okta is changed from city to l or o?From today morning, I saw this changes on my environment. With city key word, its not pulled data from Okta to Jamf.
I am starting to test JAMF Pro with Entra as the cloud identity provider for an iPad rollout. I am not the entra manager but it seems that a newly created student must change their password on first login.But when that first login is the Remote management enrolment page, their temp password doesn’t work.We don’t use JAMF Connect. Is this a known issue?
Hi Jamf Nation, While we passed a custom URL from google drive to fetch icon for the setup manager, it appears to be broken. Point to be noted, we didn't do any icon package deployment. We just passed the google drive link to fetch the icon in configuration profile under Application & Custom Settings>Jamf Applications>Icon Source Any idea what I am missing here? Thanks
Hey Jamf Nation!Jamf Pro 11.19.0 features Scoping Guardrails and Group Description Fields for Smart and Static Groups, along with Automatic Seat creation in DigiCert One TLM with SCEP Payloads, ACME Payload for macOS/iOS redistribution support, and more!How to join the beta: Enroll in the Beta Program under Product Feedback at account.jamf.com. Click “Join Community” to join the beta forum once enrolled. Please also check out this recent blog on Configuring SSO in Jamf Account prior to testing Compliance Benchmarks, Blueprints, and App Switcher.Email beta@jamf.com with questions.The beta program is covered by the Jamf non-disclosure agreement; please do not share any information regarding your testing on any public forum, including the non-beta areas of Jamf Nation. Use the Jamf Nation Beta Forum or contact Jamf via beta@jamf.com with any questions. Thank you to all who participate in this program!
Today we are releasing Jamf Pro 11.18; highlights include:Return to Service for Mobile Devices The Return to Service feature is available in the Jamf Pro interface, in addition to the Jamf Pro API. Return to Service is an option within the Wipe Device remote command that instructs a wiped device to automatically reconnect to the Wi-Fi network and re-enroll with Jamf Pro. Return to Service remembers the Wi-Fi settings and applies them automatically, which returns the device to a ready-to-use state for the next user while ensuring privacy and security among multiple users of the device. Automatic Deployment of Self Service+ for macOS Note: The option to automatically deploy Self Service+ from Jamf Pro will be made available on a regional basis in environments with Jamf Pro 11.17.1 or later. When it becomes available in your region, you will see the option in Jamf Pro. Jamf Pro enables administrators to automatically deploy Self Service+ to enrolled computers by setting Self Service+ as
When Mac users rapport issues, you always have to remove/walk to the user and typically the first you do is check log files As far I remember during Jamf training, there is an option to get log files uploaded into the jamf backend in attachement ?. But cannot remember the details on this - but is there a way to do this?
I'm new to Jamf Protect. At some point I thought I heard it can house logs, but everything I'm reading says it needs a SIEM. Can anyone clarify?
I have enabled path management notification for Google Chrome update, Today I received below notification from Jamf Pro but when I checked in Google there is no information about the mentioned version. Is this is false alert from Jamf Pro? Updates for Google Chrome are available.Title: Google ChromeVersion: 137.0.7151.121Publisher: Google
An org’s network requires non-personal devices (think digital signage, inventory scanners, etc...) to be bound to a set network using MAC address. That then requires “Private Wi-Fi Address” to be disabled on all the iOS devices otherwise the device MAC does not match up to the registered MAC.For these type devices, I have a config set to disable “Private Wi-Fi Address” but that only comes through AFTER the device is enrolled (and gets internet access of course). With a random MAC, the device cannot do the initial out of box activation and eventually times out. I can get around all of that with a USB ethernet dongle, which allows the device to get online, enroll, get wifi config settings etc... but that is time consuming.Does anyone know of a way to disable the private wi-fi address setting when you first connect a device to wifi out of the box?I have tried backing out on the setup screen and holding the wifi name in question to try and bring up options, but so far no
I'm trying to add a video to a customize enrollment. It's a video we are storing in a S3 bucket on AWS. When I try to embed it the video doesn't show. Everything I look about this is about Youtube videos but we don't particularly want to host a video on Youtube.
There's plenty of posts regarding disabling AirPlay Receiver, but we actually want to ENABLE it. Our previous AirPlay solution, AirServer, is not being properly maintained by the dev, doesn't play nice on our network, and we have just about given up on it. I tried reversing @ljcacioppo 's solution for disabling the setting here, but when set to true, it doesn't toggle the setting on; it only allows the user to enable it. This is on Seqouia 15.5. Ideally, we would like the following things set via profile: AirPlay Receiver set to ON Allow AirPlay for Anyone on the Same Network Require password set to OFF (the user must click a popup to allow the connection so this is fine) Does anyone have a working solution for this?
We use ClassLink Single Sign On to manage certain apps on our iOS devices. At first launch, you need to choose the correct school district which can get a little confusing. I was wondering if there was a way using the App Configuration setting to specify the exact URL to open upon launching ClassLink.
I'm transitioning us from Jamf Pro to Jamf School. It can't happen like a flipping a light switch so I have to deal with small amount of lingering devices still in use in Jamf Pro into the coming school year (I have all our student devices but not teacher devices). In Jamf Pro we currently have 8 different Sites each setup with their own content tokens that match our locations in Apple School Manager. As we make the transition I can't completely remove every single license from Jamf Pro's tokens, so in setting up Jamf School I'm wondering.... Should I create this same structure with new locations and new content tokens to transfer the bulk of the licenses to in Apple School Manager for the new Jamf School instance, since I can't clean house and use the existing token? Downsides? Is that what Jamf School expects or is it more tuned to one large pool of apps from one content token even when using multiple locations with Jamf School ("sites"). I suspect creating this parallel world is t
Earn a cool badge and Jamf Nation Reward Bytes for your published articles. We’re looking forward to your submissions!